Tenant admins
Find the missing piece and install it without a project: browse, review permissions, install, and hand it to the right roles.
Browse certified apps, plug-ins and vision model packs built for Docklify. Review exactly what each one can see and do, install it inside your own workspace, and manage versions, access and removal from one place.
Docklify App Marketplace is where the platform grows past what one team can build. It lists certified apps, plug-ins and user-trained small vision models made for Docklify: configuration packs that drop in ready-made reports and templates, integration apps that connect outside systems through the public API, and embedded apps that work inside Docklify pages. Every listing passes a certification review before it appears, every install happens inside your own workspace after you review its permissions, and every version stays pinned until you choose to update. Developers earn 85% of each paid sale, and tenants get the long tail of logistics software — the one report format, the one carrier link, the one check only their operation needs — without waiting on the core product.
Find the missing piece and install it without a project: browse, review permissions, install, and hand it to the right roles.
Close the gaps the core apps leave: a custom report pack, a carrier link, a check that only your floor needs.
Sell to every Docklify tenant from one listing: certification, billing and payouts handled by the platform, with 85% of each sale.
Private apps built for one tenant stay private: your own reports and integrations, installed only in your workspace.
One store, three kinds of goods. Configuration packs bundle reports, document templates, custom fields and flow rules into a single atomic install — no code, no project. Integration apps run on the developer’s own servers and connect through the versioned public API and signed webhooks, so an outside system plugs into Docklify without ever touching its database. Embedded apps work inside Docklify pages through a sandboxed frame. And vision model packs — small, user-trained detection models — list, certify and install through the same mechanism as any other app, so a model that spots a blocked aisle reaches every tenant the same way a report pack does.
Nothing appears in the catalog on a promise. Every app passes a certification checklist before it lists: real implementation, not a slide deck; declared permissions that match what the code actually asks for; a sandbox install that proves the happy path; and a review record kept with the listing. Certification lasts twelve months, and a major version — a scope change, a new endpoint, a new embedded domain — triggers a fresh incremental review. Apps that have not passed stay private: they install only in the tenant they were built for, and never appear in the public catalog.
Installing is a decision, not a click-through. The app page shows exactly what the app may see and do — which data, which scopes, which pages it embeds in — before anything installs, and the public page itself installs nothing: the install opens the App Center inside your own workspace, where you review the same list once more and confirm. Scopes are least-privilege by design, and the four money-and-stock scopes — price, billing, inventory adjustment and refunds — only ever propose; they never write directly. Consent is recorded with the install, so any later question has an answer.
An update never lands by surprise. Every install pins to the version you approved, and new versions arrive as a choice, not an ambush: staged rollout moves a version tenant by tenant, the certification record follows the version, and the public API carries a deprecation window so an app built against an old version keeps working while its developer catches up. If a version misbehaves, the pinned version is the rollback point — reinstall the known-good build and the workspace is back where it was, with the whole history in the audit log. The developer sees the same rollout state you do, so a question about a version has one answer on both sides.
Every install has an off switch. If an app misbehaves, the platform or the tenant stops it per tenant, near-instantly — no redeploy, no ticket queue, no waiting for the developer to answer. Uninstalling removes the app’s data from the tenant: configuration copies the tenant never changed are reclaimed, copies the tenant edited stay theirs and are listed in the removal result, and nothing is deleted silently. Consent snapshots and the audit trail stay on file for twenty-four months, so a dispute a year later still has evidence. The switch itself is tiered: stop one tenant, stop a version everywhere, or stop the app outright — each level logged with who pulled it and when.
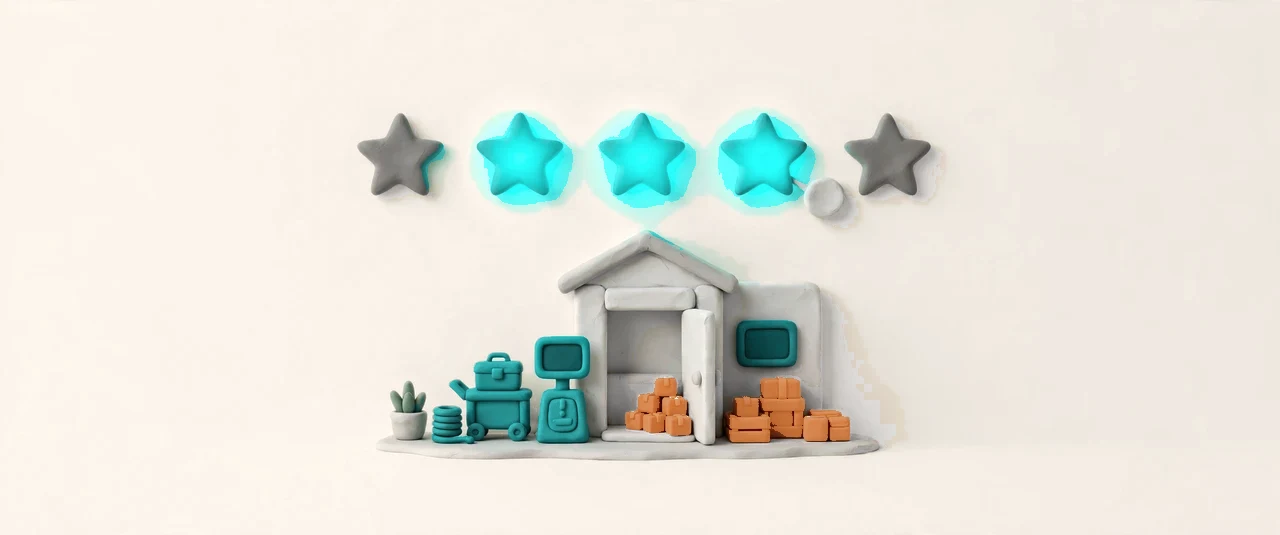
The catalog shows what tenants actually think, not what a listing claims. Each organization rates an app once, on a one-to-five scale, with an optional private note that never goes public; there are no public text comments to game. The average appears only once three organizations have rated, shown to one decimal with the count and the star distribution beside it. Install counts never show exact numbers — only bands: under ten, ten-plus, fifty-plus, one hundred-plus, five hundred-plus — so a small app is not punished for being new, and a big number cannot be faked by a single tenant.
The split is simple, and it is the industry’s: the developer keeps 85%, the platform keeps 15%. Settlement runs monthly on the net amount — Stripe channel fees and refunds come off first — with a fifty-dollar minimum payout and Stripe Connect transfers, and a refund in one month offsets the next month’s payout instead of disappearing. Tenants pay in dollars, converted from their Credit wallet at one Credit to one cent, and a plug-in fee only ever draws from purchased balance, never from the monthly allowance. The books keep developer receivables, platform share, channel fees and refund offsets in four separate ledgers.
Reports, templates, fields and rules as one atomic pack — validated whole, installed whole.
Developer-hosted apps that connect through the public API and signed webhooks.
Working pages that run inside Docklify in a sandboxed frame.
OAuth scopes with server-enforced tenant isolation on every call.
Signed events delivered to apps, with dead-letter handling when delivery fails.
The public side stays closed until the platform opens it; private installs always work.
Test installs and review evidence before a listing goes live.
Installs, consent, version changes and removals — every step recorded.